The Governance Layer
for the AI Agent Era.
SafeLoc builds the CAM Protocol, an enterprise API that requires multi-party human approval before AI agents access sensitive data or carry out high-risk actions.
Built for consequential actions in financial services, cybersecurity and critical infrastructure.
Collaborative Access Management
Human approval, before an AI action executes.
CAM puts an approval gate in front of a sensitive operation. Designated people review the request, a configured quorum must approve, and any one member can veto. Authorization expires after use, and the decision is recorded for audit.
Office, home, and everywhere in between. Every approval is recorded the same way.
Built for what you're governing
One protocol. Every governed surface.
Choose Your Governed Surface
Multi-party human approval over AI-driven access to client data, portfolios, and asset movements.
Mandatory quorum before any AI-initiated access to client accounts or portfolios
Before an AI agent or operator can access sensitive client data, portfolio positions, or execute asset movements, M-of-N approval from a configurable set of authorized principals is required. No single advisor or automated agent can unilaterally authorize access.
Veto evaluated before the approval counter
CAM's Single-Denial Veto gives compliance officers and risk managers a block that fires before quorum completes. A single flagged approver stops the action immediately. Enforcement happens at the protocol layer, by design, not by policy.
Supports fiduciary accountability with a hash-chained audit log
Every authorization request, approval, denial, and execution is append-only and cryptographically-anchored. Both the advising firm and the compliance function hold independent read access. No operator has write capability post-commit.
Ephemeral access to account and position data
Sensitive client account data and position records are released only at the moment threshold conditions are satisfied, and only for the duration of a time-bound token. An attacker who defeats the governance layer finds no persistent data surface.
Featured Capabilities
How It Works Through MCP + REST
High-value transaction initiated
MCP or REST request enters the governance layer for evaluation against configured quorum policy.
M-of-N approvers authorize. Veto check runs first. Any denial blocks immediately.
Time-bound token issued. Data released only now. Immutable audit entry written.
All events enter an append-only bilateral audit log. Neither party has write access.
Live Protocol Demo
Watch CAM govern a real access request, start to finish.
An AI agent requests access. A human Circle decides. Any member can veto. Watch all four patent-pending elements execute live.
FINANCIAL SERVICES · HEALTHCARE · AI AGENT GOVERNANCE · ENTERPRISE & WORKFORCE · M-OF-N QUORUM · SINGLE-DENIAL VETO · EPHEMERAL RELEASE · BILATERAL AUDIT
Open interfaces
Works with your stack
CAM is a REST API. Anything that can make an HTTPS call can be governed: AI agent frameworks, internal tools, workflow automation platforms, and custom applications.
Developer detailsA focused path forward
How a pilot works
A practical sequence from workflow discovery to carefully scoped production use.
- 01
Discovery: we map the sensitive actions and who should approve them.
- 02
Integration scoping: we define the API touchpoints, quorum rules and audit needs.
- 03
Pilot: CAM governs a real workflow in a limited environment.
- 04
Production: expand to more actions and teams with full audit coverage.
Incidents we track
Publicly reported incidents and security research involving stolen credentials, connected tools, software supply chains, and AI agents. Each point marks one documented entry; the comparison is about reported activity, not a claim that CAM changed an event.
--
Days since the last major incident
Sept 21, 2026
26
Incidents we track since mid-2024
Updated October 2026
7
In the last quarter alone
Q3 '26
Reported incidents by quarter
· Autonomous AI agent breaches DIVD: An agent chained two unknown flaws to go from a hijacked session to root in seconds. Cloud Security Alliance (opens in a new tab)
The acceleration
More than 1 in 8 reported AI breaches now involve autonomous agents, per HiddenLayer's 2026 AI Threat Landscape Report. One AI-agent campaign compromised 395 organizations in 48 countries, 11 of them in 26 seconds. BleepingComputer (opens in a new tab)Source: HiddenLayer, 2026 AI Threat Landscape Report
Compliance Diagnostic
CAM Compliance Diagnostic
Answer 3 questions. Get an instant verdict on whether your enterprise needs CAM, and how it maps to your regulatory exposure.
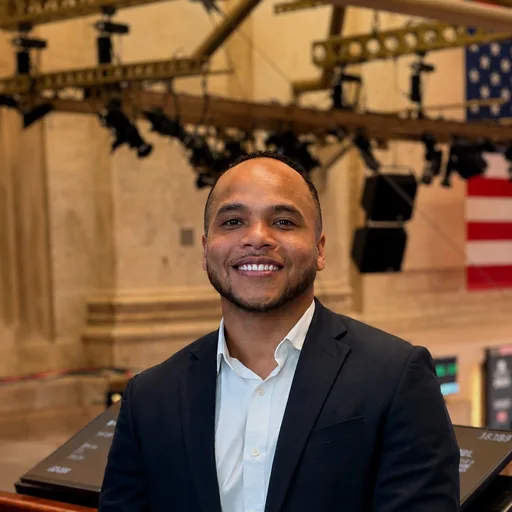
LeAndrew Gordon
Put human oversight before sensitive AI actions.
CAM is being built so AI can do consequential work with the right people in the loop.
 AI Champion, Askraa
 Chapter Lead, The AI Collective Fort Worth
- Replit Top 25 AI Builder
- Patent-pending, confirmed novel by NYLS Patent Law Clinic
- GFI Conference panelist, Nov 2026
Let's build
Building something with AI? Let's talk.
Whether you’re a regulated firm exploring CAM, a team wanting to put AI to work safely, or a builder with an idea, reach out. LeAndrew personally reads every message.